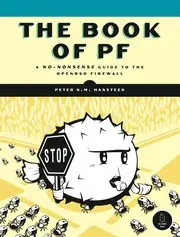
The Book of PF
Peter N. M. Hansteen · 2008
Programming and computer science › Operating systems and networking
#6,992 most recommended
Hacker News
5
mentions by 5 people · top 48% of 15,732 books
Open Library
—
No ratings yet
2 want to read
Wikipedia
—
No article yet
About the book
A practical guide to pf, the packet filter firewall in OpenBSD, covering how to write its rule sets, filter and translate traffic, and run it on a server or gateway. It also covers the TCP/IP background needed to understand what the rules do, and its scope extends to related BSD systems such as Mac OS X. The book holds that a capable firewall can be configured clearly by a systems administrator who works through concrete examples, without needing the scattered documentation that usually surrounds such tools. It presents pf's rule syntax and stateful filtering as readable once the underlying network behaviour is understood. It also treats firewall setup as a matter of disciplined administration, meaning careful rule design, testing, and logging, rather than a one-off configuration step.
Written by Claude from what it knows of this book.
What Hacker News says 40% recommend · 0% critical
In the commenters’ own words
Human readable syntax. Documentation. A complex iptables ruleset is difficult to understand, while a pf.conf almost reads like prose. Feature-wise, netfilter…
Thanks for mentioning it. If this is it, it's in O'Reilly's Safari catalog (I've no association, just a Safari account): The Book of PF, 3rd Edition By: Peter…
What Open Library readers say
No Open Library reader has rated it yet.
- 2 want to read
- 0 reading
- 0 have read
What critics say, via Wikipedia
No Wikipedia article about this book yet, so no critics to quote.
Reddit communities — coming later
Details
- First published
- 2008
- ISBN
- 9781593275891
- Editions known
- 8 at Open Library
- Open Library
- OL12421886W
Computer networksComputer securityFirewalls (Computer security)ManagementOpenBSDOperating systems (computers)TCP/IP (Computer network protocol)
Read next: its neighbours on the mosaic
 Linux FirewallsSteve Suehring · 2005 · recommended by 3 people · similar by subject and what people say about it
 Absolute OpenBSDMichael W. Lucas · 2003 · recommended by 11 people · similar by subject and what people say about it
 Absolute FreeBSDMichael W. Lucas · 2008 · recommended by 8 people · similar by subject and what people say about it
 The design and implementation of the FreeBSD operating systemMarshall Kirk McKusick · 2004 · recommended by 36 people · similar by subject and what people say about it
 UNIX filesystemsSteve D. Pate · 2003 · recommended by 3 people · similar by subject and what people say about it
 TCP/IP Illustrated, Volume 1Kevin Fall · 2024 · recommended by 17 people · similar by subject and what people say about it
 FreeBSD device driversJoseph Kong · 2012 · recommended by 4 people · similar by subject and what people say about it
 Advanced programming in the Unix environmentW. Richard Stevens · 1992 · recommended by 100 people · similar by subject and what people say about it
 UNIX for super-usersEric Foxley · 1985 · recommended by 1 person · similar by subject and what people say about it
 Unix Network ProgrammingW. Richard Stevens · 1990 · recommended by 54 people · similar by subject and what people say about it
 The art of UNIX programmingEric S. Raymond · 2003 · recommended by 85 people · similar by subject and what people say about it
 The TCP/IP GuideCharles Kozierok · 2005 · recommended by 11 people · similar by subject and what people say about it
 SSH MasteryMichael W. Lucas · 2012 · recommended by 4 people · similar by subject and what people say about it
 TCP/IP IllustratedW. Richard Stevens · 1994 · recommended by 58 people · similar by subject and what people say about it
 Unix System Administration HandbookEvi Nemeth · 1989 · recommended by 6 people · similar by subject and what people say about it
 Internetworking with TCP/IPDouglas E. Comer · 1988 · recommended by 12 people · similar by subject and what people say about it
 Essential System AdministrationÆleen Frisch · 1991 · recommended by 12 people · similar by subject and what people say about it
 BPF Performance ToolsBrendan Gregg · 2019 · recommended by 15 people · similar by subject and what people say about it
 Advanced UNIX programmingMarc J. Rochkind · 1985 · recommended by 12 people · similar by subject and what people say about it
 InterconnectionsRadia Perlman · 1992 · recommended by 13 people · similar by subject and what people say about it
 UNIX in a NutshellArnold Robbins · 1999 · recommended by 7 people · similar by subject and what people say about it
 UNIX and Linux system administration handbookEvi Nemeth · 2010 · recommended by 35 people · similar by subject and what people say about it
 Understanding Linux network internalsChristian Benvenuti · 2005 · recommended by 2 people · similar by subject and what people say about it
 The Elements of Networking StyleM. A. Padlipsky · 1984 · recommended by 8 people · similar by subject and what people say about it